Hackers stole Pentagon personnel records of over 3 million people
Hackers stole Pentagon personnel records of over 3 million people Read More »
Metamask discloses security incident affecting its infrastructure Read More »
Russian state hackers use new RedFlick technique to push malware Read More »
DIVD says Zammad zero-days enabled AI-driven network breach Read More »
This year at Microsoft Ignite, we spotlight our AI-first, end-to-end security platform designed to protect identities, devices, data, applications, clouds, infrastructure, and the AI agents now working alongside your teams.
The post Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 appeared first on Microsoft Security Blog.
Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 Read More »
Over 543,000 valid credentials exposed in public GitHub repositories Read More »
CISA warns of critical pre-auth RCE flaw in MikroTik RouterOS Read More »
Cisco warns of new SD-WAN zero-day exploited in attacks Read More »
AI’s Third Wave: Coworkers Break the Security Model That Worked for Agents Read More »
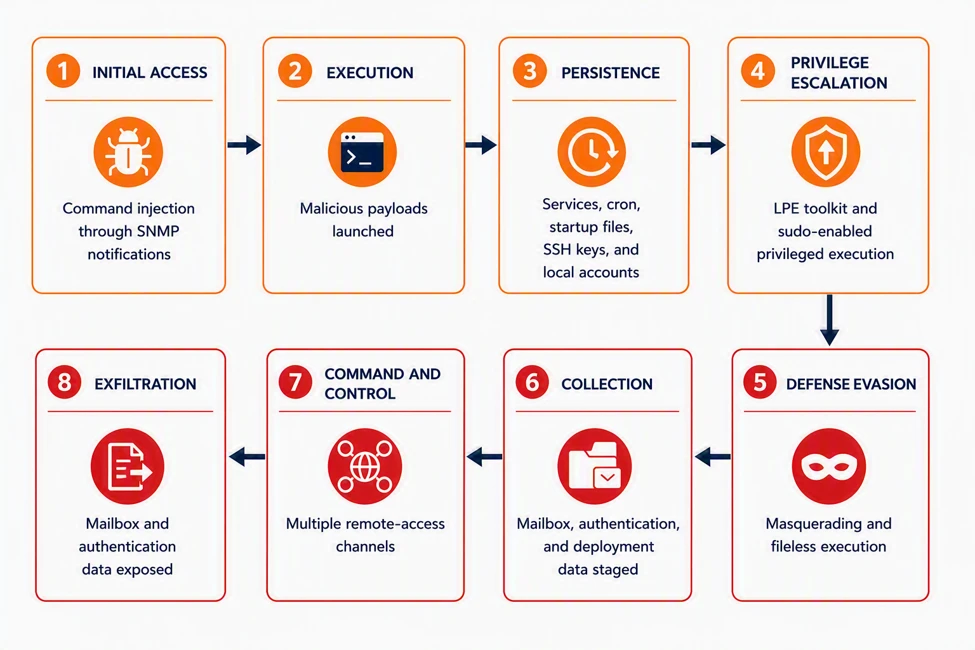
Microsoft Threat Intelligence examines CVE-2026-73570 exploitation in Zimbra, including observed attack paths, detection opportunities, and mitigation guidance.
The post Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 appeared first on Microsoft Security Blog.