Microsoft

The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime

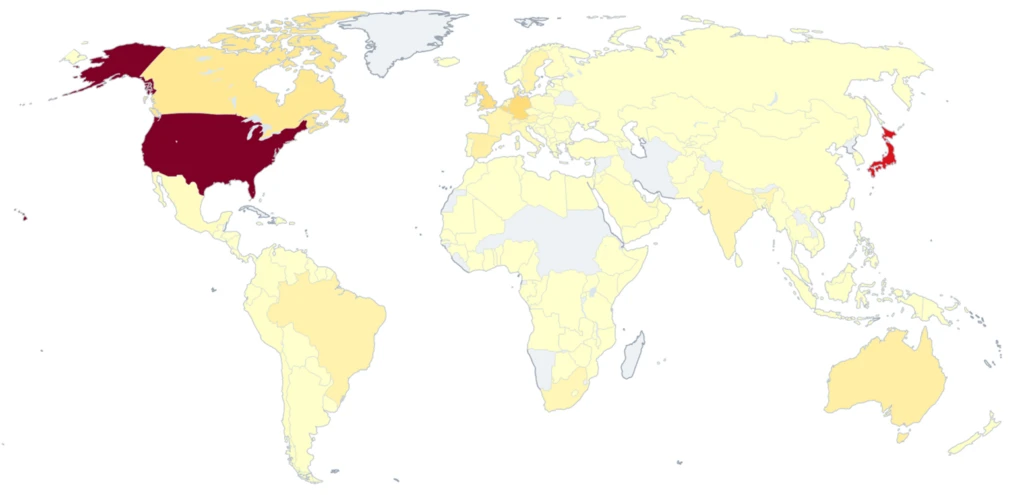
Microsoft uncovered a Chinese-language cybercriminal ecosystem, an interconnected network of phishing kit operators (tracked as Storm-2990), and an illicit marketplace (tracked as Storm-3119) selling tools and infrastructure for large-scale phishing. In collaboration with law enforcement agencies and other partners worldwide, Microsoft’s Digital Crimes Unit (DCU) facilitated a disruption of the ecosystem.

The post The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime appeared first on Microsoft Security Blog.

The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime Read More »

Post-quantum authentication: Why organizations should start testing certificate ecosystems now

Prepare for post-quantum authentication by testing certificate ecosystems now. Learn how Microsoft’s PQC TLS Pilot Program helps advance future readiness.

The post Post-quantum authentication: Why organizations should start testing certificate ecosystems now appeared first on Microsoft Security Blog.

Post-quantum authentication: Why organizations should start testing certificate ecosystems now Read More »

Preparing governments for an era of interconnected cyber risk

According to this year’s Microsoft Digital Defense Report, government agencies and services were the sector most impacted by cyber threats in 2026, accounting for 27% of observed activity, up from 17% in 2025.

The post Preparing governments for an era of interconnected cyber risk appeared first on Microsoft Security Blog.

Preparing governments for an era of interconnected cyber risk Read More »

​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026

This year at Microsoft Ignite, we spotlight our AI-first, end-to-end security platform designed to protect identities, devices, data, applications, clouds, infrastructure, and the AI agents now working alongside your teams.

The post ​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 appeared first on Microsoft Security Blog.

​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 Read More »

Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570

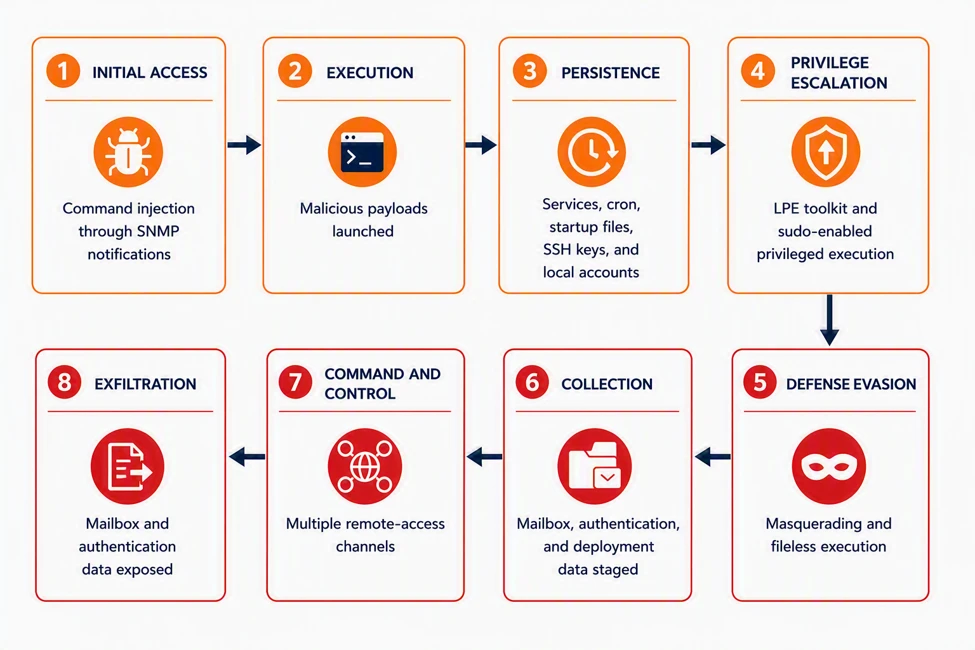
Microsoft Threat Intelligence examines CVE-2026-73570 exploitation in Zimbra, including observed attack paths, detection opportunities, and mitigation guidance.

The post Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 appeared first on Microsoft Security Blog.

Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 Read More »