Microsoft

Star Blizzard refines phishing and malware delivery with the RedFlick technique

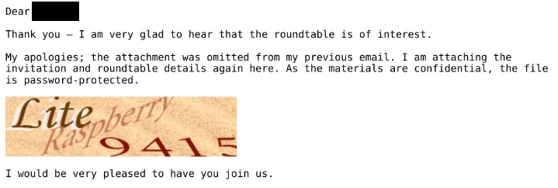
Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing campaigns, the use of accounts on compromised websites, and a novel malware delivery technique, tracked by Microsoft as “RedFlick”.

The post Star Blizzard refines phishing and malware delivery with the RedFlick technique appeared first on Microsoft Security Blog.

Star Blizzard refines phishing and malware delivery with the RedFlick technique Read More »

NeedyMantis: Unpacking a post-compromise malware family used in targeted operations

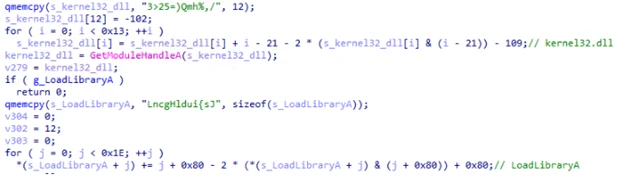
Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions that combines custom loaders, encrypted archives, and extensible components to maintain long-term access and support follow-on operations.

The post NeedyMantis: Unpacking a post-compromise malware family used in targeted operations appeared first on Microsoft Security Blog.

NeedyMantis: Unpacking a post-compromise malware family used in targeted operations Read More »

Storm-3168: Agentic-driven cloud attacks using compromised service principals

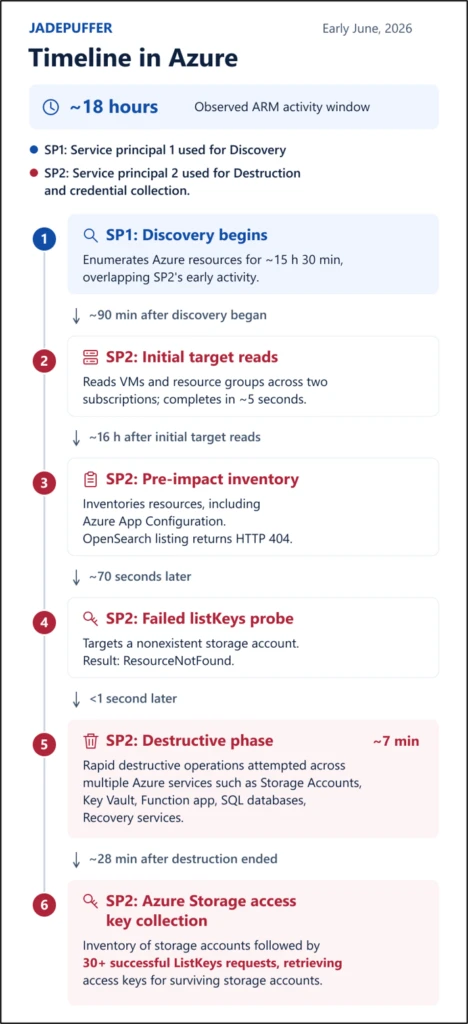
Microsoft details JADEPUFFER-linked Azure reconnaissance, resource deletion, and credential access using compromised service principals, identifying the activity as associated with Storm-3168 and providing guidance for defenders.

The post Storm-3168: Agentic-driven cloud attacks using compromised service principals appeared first on Microsoft Security Blog.

Storm-3168: Agentic-driven cloud attacks using compromised service principals Read More »

Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments

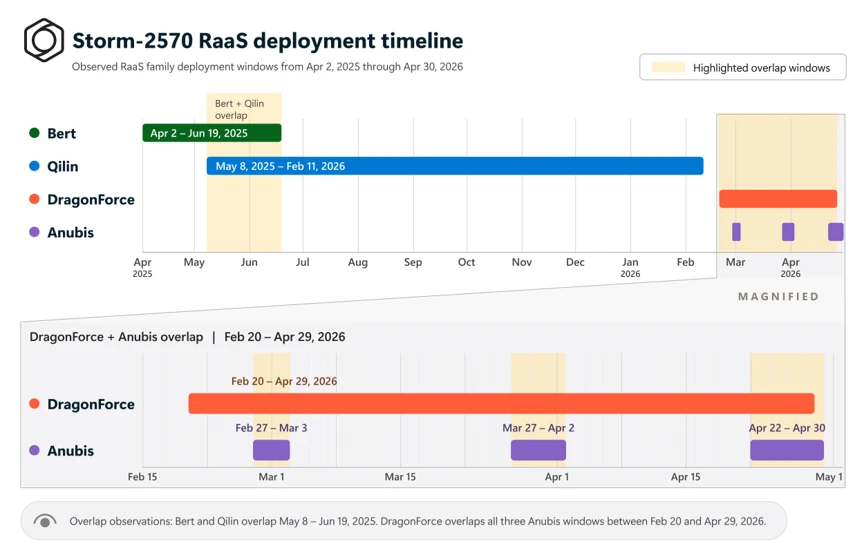
Storm-2570 is a ransomware affiliate that uses consistent post-compromise tools and techniques across deployments involving Qilin, DragonForce, Anubis, and BERT ransomware, and provides guidance to help defenders detect and disrupt this activity before ransomware deployment.

The post Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments appeared first on Microsoft Security Blog.

Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments Read More »