​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026

This year at Microsoft Ignite, we spotlight our AI-first, end-to-end security platform designed to protect identities, devices, data, applications, clouds, infrastructure, and the AI agents now working alongside your teams.

The post ​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 appeared first on Microsoft Security Blog.

​​Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026 Read More »

AI’s Third Wave: Coworkers Break the Security Model That Worked for Agents

Persistent AI coworkers may operate continuously with standing access, creating identity risks that existing security models were not designed to handle. Token Security explains why these agents need their own identities, owners, scoped permissions, and lifecycle controls. […]

AI’s Third Wave: Coworkers Break the Security Model That Worked for Agents Read More »

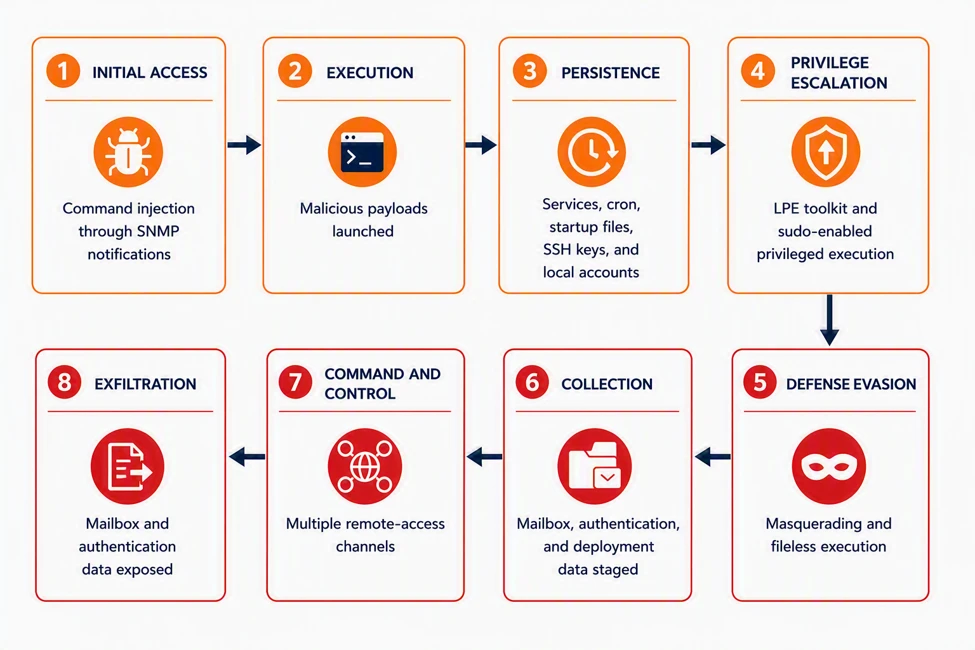
Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570

Microsoft Threat Intelligence examines CVE-2026-73570 exploitation in Zimbra, including observed attack paths, detection opportunities, and mitigation guidance.

The post Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 appeared first on Microsoft Security Blog.

Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570 Read More »