Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments

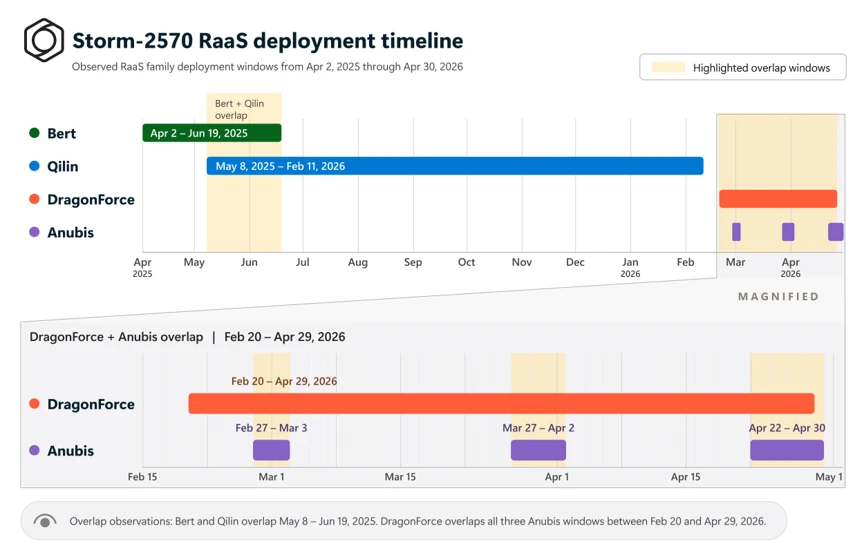
Storm-2570 is a ransomware affiliate that uses consistent post-compromise tools and techniques across deployments involving Qilin, DragonForce, Anubis, and BERT ransomware, and provides guidance to help defenders detect and disrupt this activity before ransomware deployment.

The post Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments appeared first on Microsoft Security Blog.

Beyond the ransomware: Tracking Storm-2570’s consistent tradecraft across deployments Read More »

FedRAMP VDR & VER: Daily Scans Are Only the Beginning

FedRAMP’s new VDR and VER requirements make vulnerability management more continuous, with faster scanning, tighter remediation deadlines, and stronger evidence requirements. Anecdotes explains why the December 7 deadline is just the beginning of a broader shift toward continuous, automated compliance validation. […]

FedRAMP VDR & VER: Daily Scans Are Only the Beginning Read More »